Operational Continuity · Tender Ready

Ensuring Operational Continuity in an Interconnected Sky and SMART Airport.

AeroCy bridges the critical gap between flight safety and digital security — a comprehensive protective envelope that keeps aviation infrastructure resilient and regulator-ready.

Aircraft airborne now
—
Live · OpenSky Network
SCROLL
The Reality

Aviation's digital perimeter is 100% exposed.

Every airline, airport, and ground operator runs on an interconnected ecosystem of IT, OT, IoT, e-Operations, and supply-chain vendors. A single compromised vendor is a path into the cockpit.

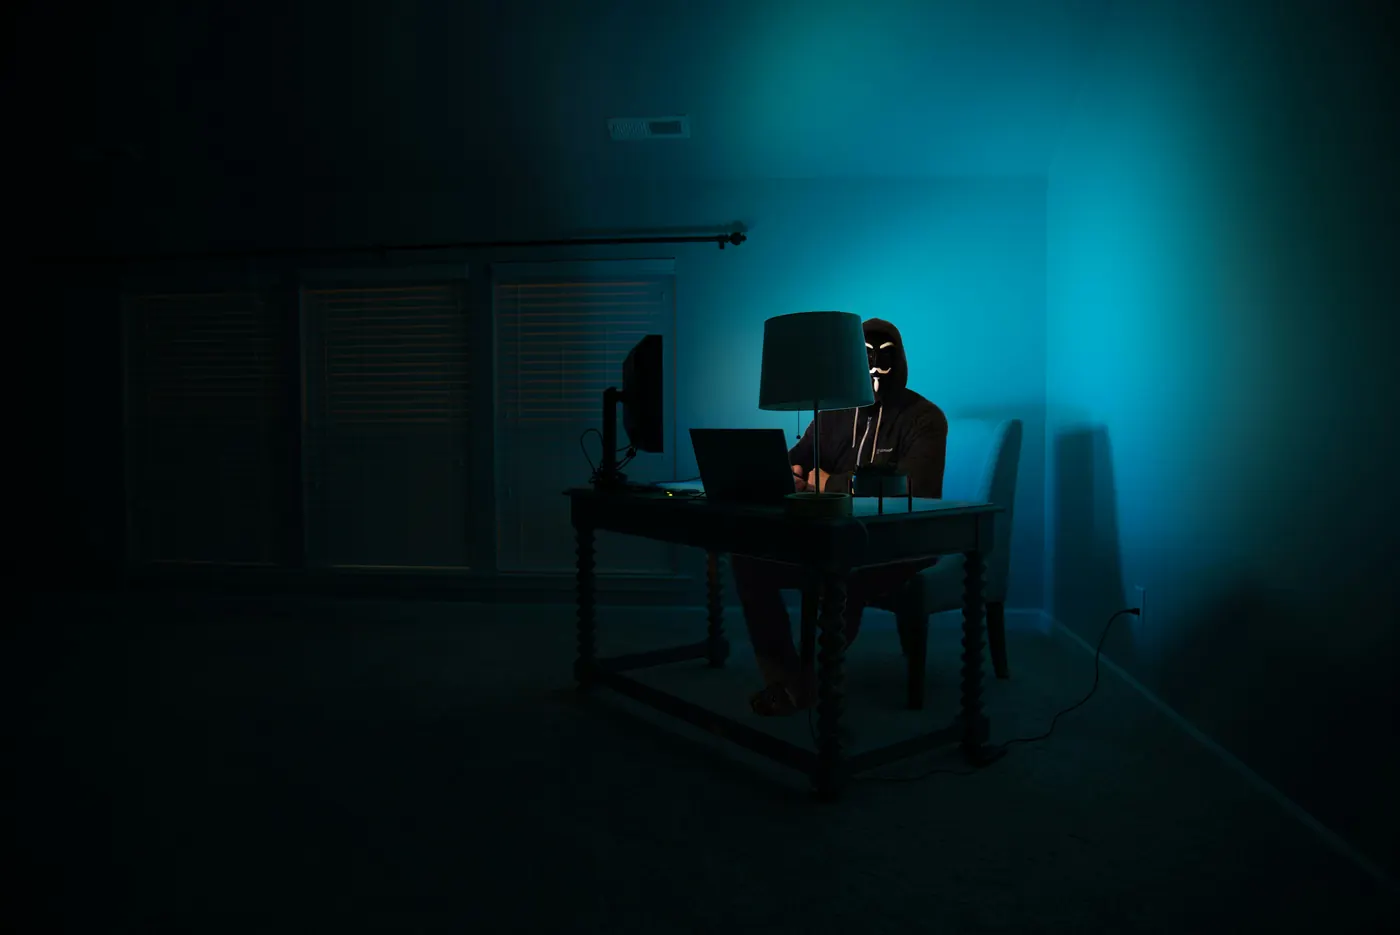
A hooded figure illuminated by cyan monitor light — representing the threat actor
◉ ACTIVE THREAT VECTOR
Supply-chain exposure
0%
of aviation organisations are exposed via their supply chain — even with hardened perimeters.
Detection rules deployed
0+
civil-aviation-specific correlation rules running from day one.
SOC coverage
0/7
continuous SIEM/SOC integration with real-time, AI-driven rule updates.
AVSEC heritage
0YR
three decades of intelligence-driven aviation security operations.

This isn't theoretical.
It's the public record.

Five disclosed aviation cyber incidents in the last decade. Real organisations. Real damage. All publicly reported.

2023
RANSOMWARE

Boeing — LockBit ransomware attack

The LockBit ransomware group breached Boeing's parts and distribution business, exfiltrating ~43GB of internal data after Boeing declined to pay. The data was published on LockBit's leak site.

Source: BleepingComputer →
2021
SUPPLY CHAIN

SITA — passenger-data breach

SITA's Passenger Service System was breached, exposing frequent-flyer records from dozens of airlines including Singapore Airlines, Lufthansa, Air India, and others. A textbook supply-chain compromise.

Source: BBC News →
2020
DATA BREACH

easyJet — 9M customer records exposed

A "highly sophisticated" cyber attack exposed personal data of 9 million customers and credit-card details of 2,208. The carrier faced a multi-million-pound class action.

Source: BBC News →
2018
MAGECART

British Airways — 380k card details stolen

A Magecart-style web skimmer was injected into BA's payment flow, capturing 380,000 customer card records over 15 days. The ICO ultimately fined BA £20M.

Source: UK ICO →
2015
OPERATIONAL DOWNTIME

LOT Polish Airlines — flight-plan systems grounded

A DDoS attack on LOT's flight-planning infrastructure grounded ~10 flights and stranded ~1,400 passengers at Warsaw Chopin. One of the first publicly acknowledged "operational" aviation cyber events.

Source: Reuters →

The loopholes attackers actually use

01
Supply-chain vendor access
Third-party booking, catering, ground-handling, and MRO systems — all with privileged network access, often without parity-grade security.
02
EFB & cockpit-adjacent devices
Electronic Flight Bags carry mission-critical data and frequently sync with airline backends over public networks at the gate.
03
ADS-B & legacy protocol exposure
Unauthenticated broadcast protocols still underpin parts of air-traffic awareness. Spoofing and jamming research is publicly documented.
04
e-Operations & passenger systems
Loyalty programs, check-in, baggage, and PSS environments hold richer personal data than most realise — and are the most frequently breached.

All incidents cited are publicly disclosed. Sources link to the original reporting. AeroCy makes no claim of involvement in any of the above — they are presented as evidence of the threat environment in which aviation operates.

The AeroCy Solution

A protective envelope, built on three pillars.

Not generic cybersecurity bolted onto aviation. A holistic resilience layer purpose-built for the protocols, regulators, and operational realities of civil aviation.

01 · PILLAR

Risk-based

Prioritise the critical assets and high-impact scenarios — not the loudest alerts. Resources flow to what would actually ground operations.

02 · PILLAR

Threat-oriented

Focus on the actual adversaries and attack vectors targeting aviation — APTs, supply-chain actors, ransomware crews — not a generic threat library.

03 · PILLAR

Intelligence-driven

Self-collected aviation intel fused with global threat intelligence — preempting attacks before they touch your fleet, terminal, or vendor network.

There is no flight safety
without digital security.

Four services. One envelope.

01 · Monitoring

Hybrid Threat Monitoring

Continuous detection across IT, OT, IoT, e-Operation, and data layers — the only kind of monitoring that catches threats moving between worlds.

Learn more →
02 · Supply Chain

Vendor Shield

Supply-chain hardening for the 100% exposed perimeter. Continuous vendor risk scoring, contractual compliance enforcement, and isolation playbooks.

Learn more →
03 · Compliance

Regulatory Compliance & Audit

ICAO, IATA, EASA, ACI, FAA — the audit package, the evidence trail, the tender-ready posture. Compliance as a defensible operational state.

Learn more →
04 · Crisis

Crisis Management & Resilience Testing

Tabletop exercises, red-team engagements, and EFB penetration testing. Including the tests regulators ask about and most consultants quietly skip.

Learn more →
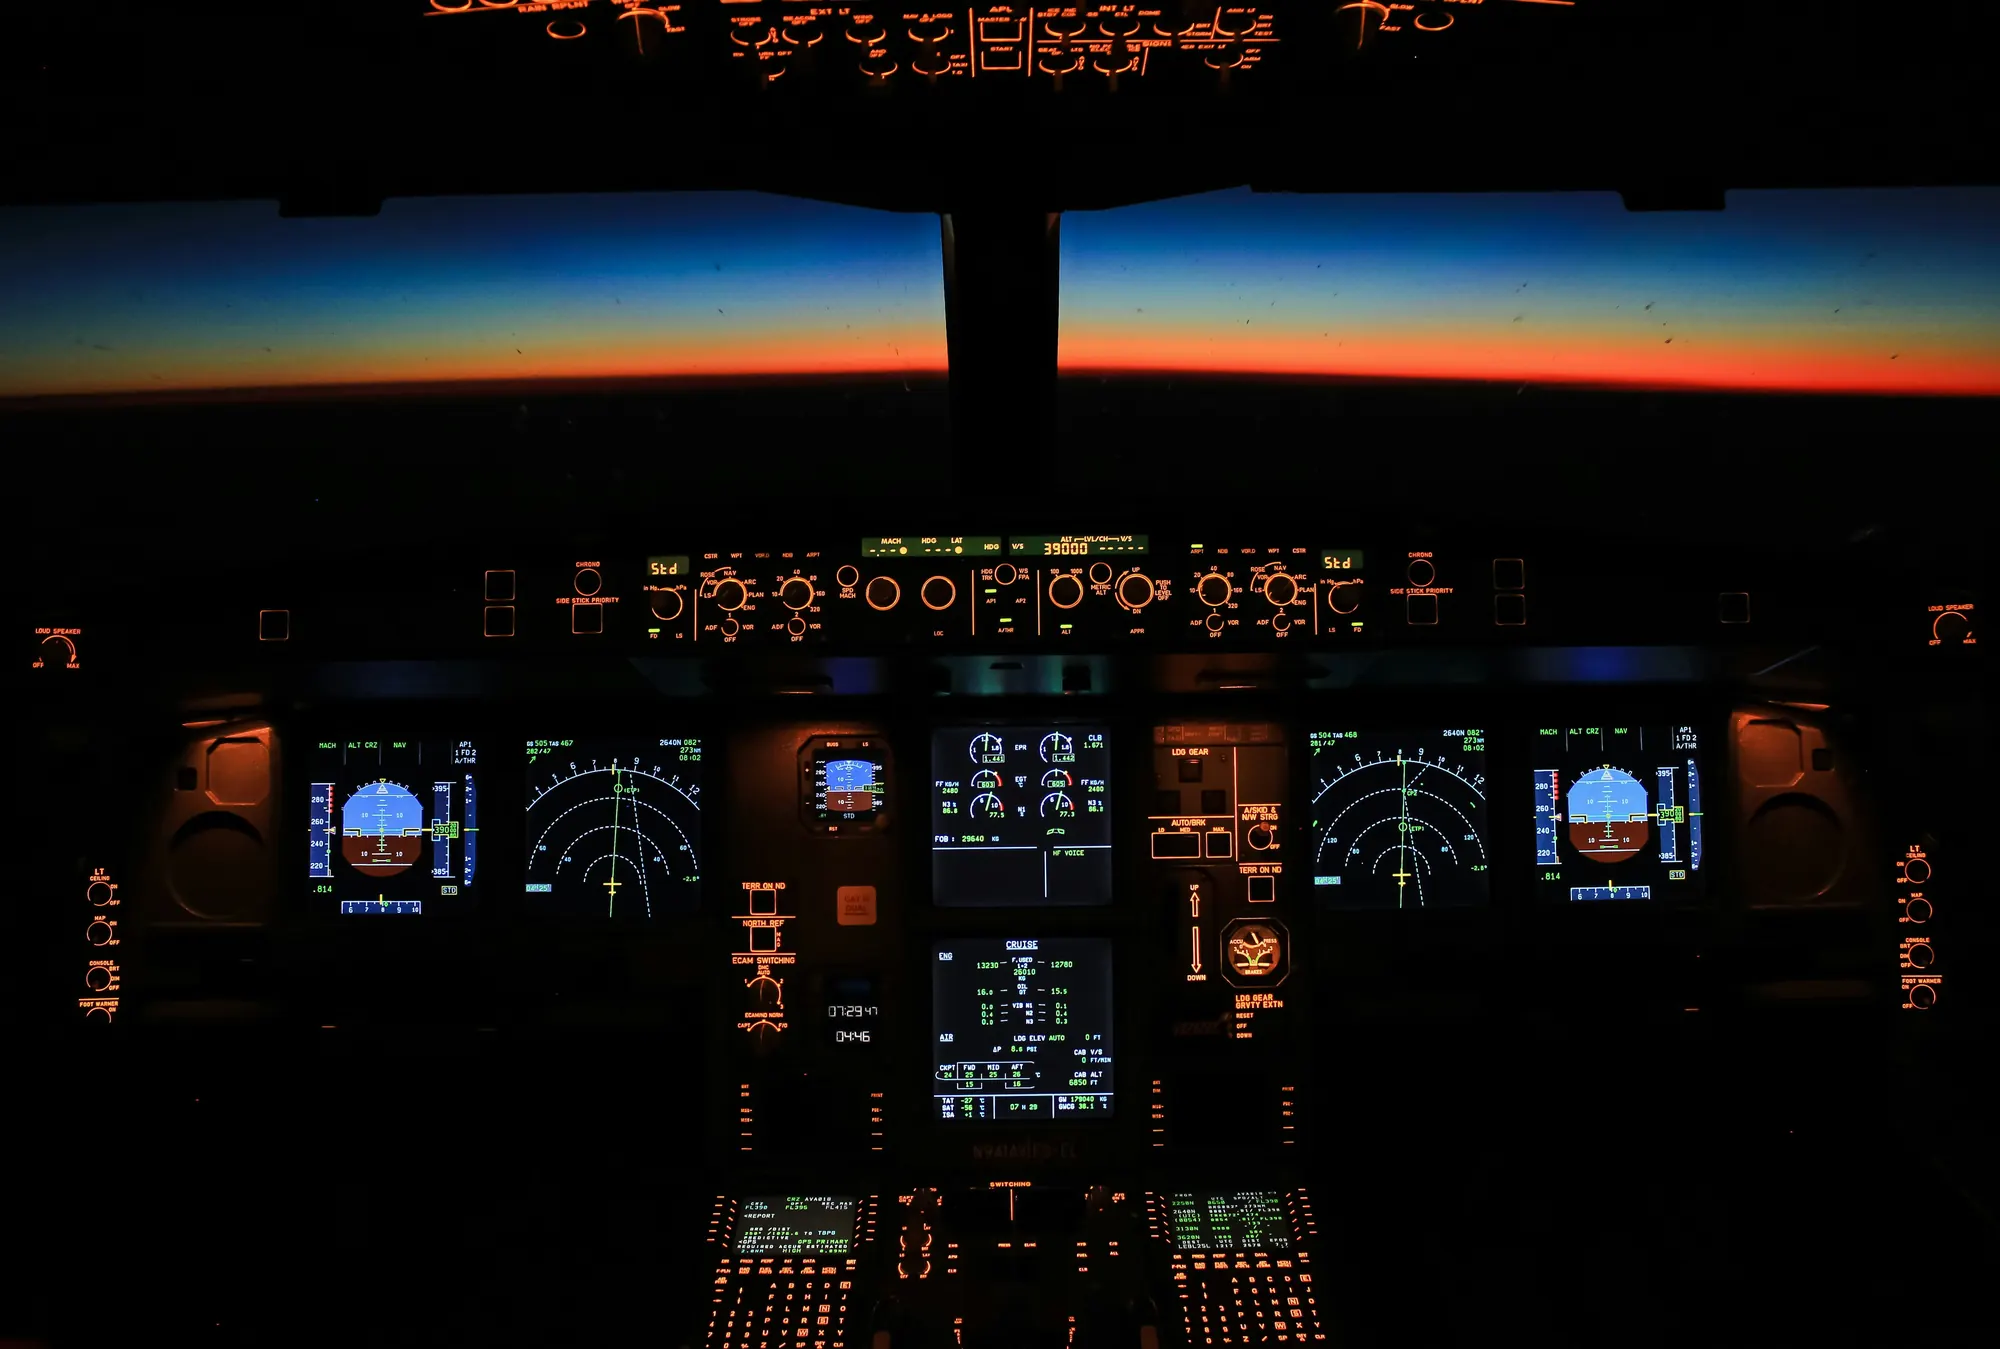
Aircraft cockpit instrumentation at altitude
◉ COCKPIT-CRITICAL
Technology

State-grade detection, aviation-tuned.

CyRay's national-infrastructure detection engine — adapted, hardened, and pre-loaded with civil aviation's most adversary-relevant rule set.

  • Approved by the Israeli government to protect Israeli airlines.
  • Active protection at Ben-Gurion Airport.
  • 1,000+ civil-aviation detection rules deployed from day one.
  • Full SIEM/SOC integration with continuous real-time rule updates, fully AI-driven.
  • IT/OT Fusion adapted to aviation protocols — the only architecture that sees the whole attack path.
Trusted by
Israel MOT
Arkia
Israir

Let's talk.

Whether you're scoping a risk assessment, evaluating a POC, or exploring a strategic partnership — start a conversation with our team.